Calendar of Events


Webinar | How AWS Continuum and Amazon Inspector Cover the Full Vulnerability Spectrum
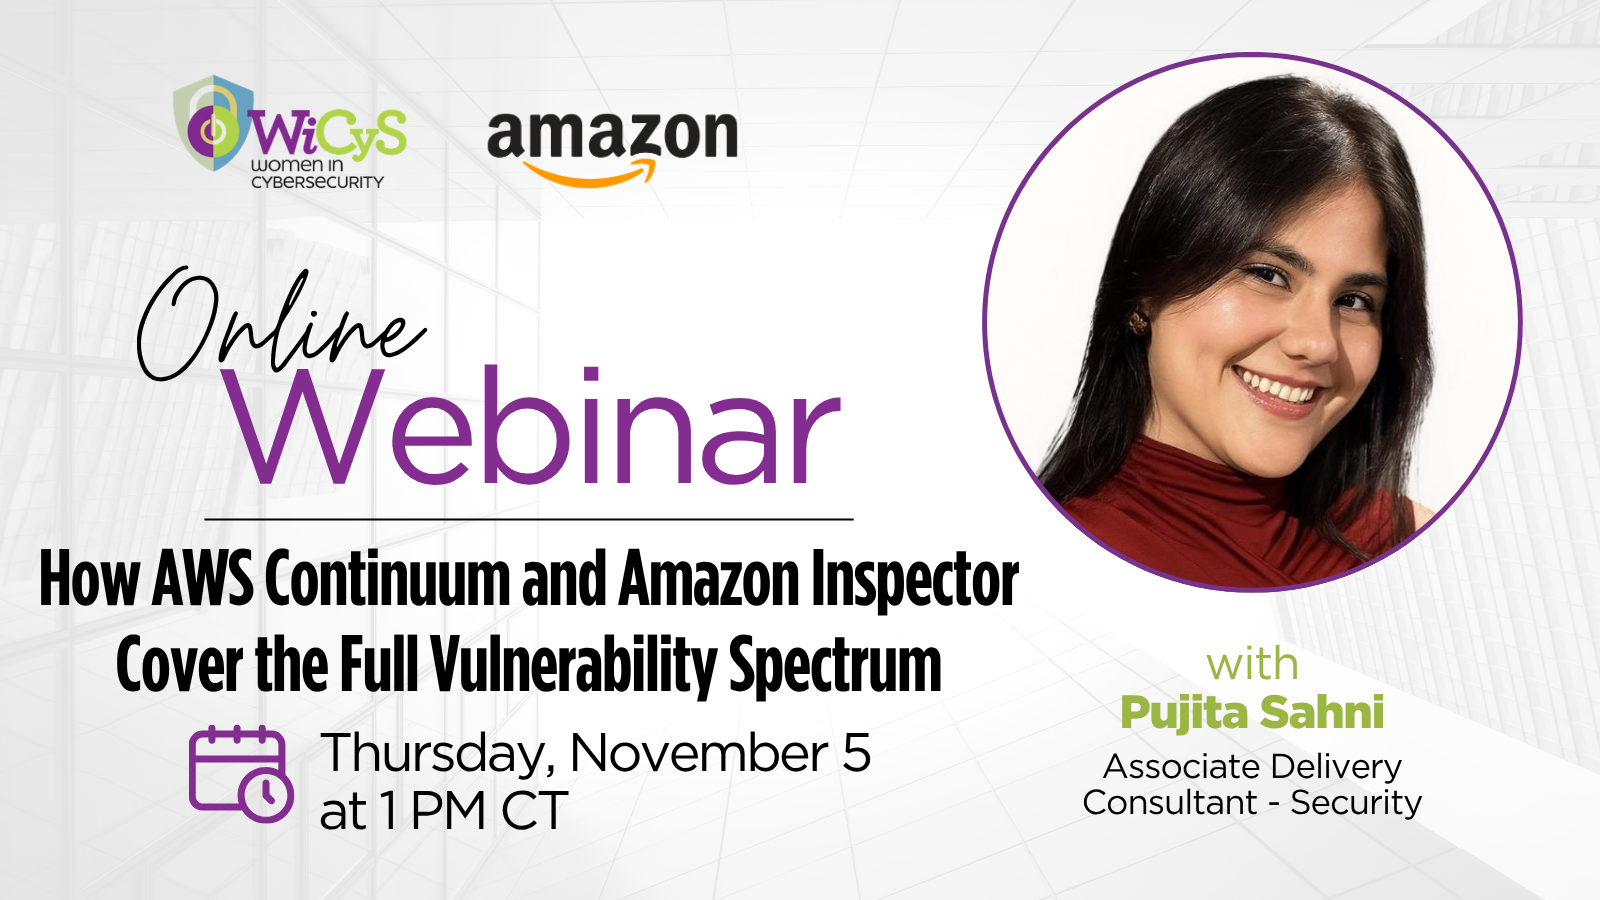
60% of organizations update web applications weekly, yet 75% test security monthly or less, leading 81% to knowingly ship vulnerable code to meet deadlines, driven by traditional pen tests taking three weeks and $25–50K per engagement.
In this WiCyS webinar, Amazon Web Services demonstrates how to close this gap using two complementary security solutions:
AWS Security Agent (The Unknown): A frontier AI agent that proactively secures applications across the SDLC—reviewing design docs, enforcing PR policies, and executing multi-step pen tests in hours to catch business logic flaws and architectural weaknesses pattern-matchers miss.
Amazon Inspector (The Known): An automated vulnerability management platform that continuously scans EC2, Lambda, containers, and repositories to track the 80% of vulnerabilities that are documented—including CVEs, network exposure, IaC misconfigurations, and CIS benchmark violations.
Attendees will learn where these services overlap, where they diverge, and how to combine both into a unified security program via AWS Security Hub.
——————
WiCyS is proud to provide members the opportunity to earn CPE/CEU credits for attending WiCyS Webinars live. To earn CPE/CEU credits with the following providers, you must meet the minimum requirements:
- GIAC/(ISC)2: attend for a minimum of 45 minutes or the entirety of the webinar
- CompTIA: attend for a minimum of 60 minutes or the entirety of the webinar (webinar topic must relate to the certificate being renewed)
Attendees who meet the requirements can log into BrightTALK to print out their attendance certificates to submit for CPE/CEU credits.
Register for this webinar and view the recording if you are unable to join live.